Hi Everyone... ဒီကနေ့တော့ VPC Peering လုပ်တဲ့ အကြောင်းလေးပြောပြပေးသွားမှာပါ။
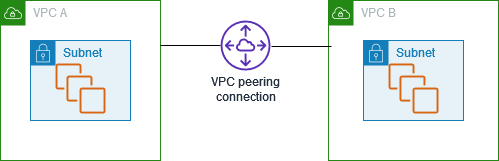
VPC peering ဘာလို့လုပ်တာလဲ ဘယ်အချိန်တွေမှာသုံးတာလဲဆိုတာကို ကြည့်ရအောင်...
သိတဲ့ အတိုင်း ပဲ AWS networking မှာ VPC ကမပါမဖြစ်အရေးပါပါတယ်
AWS account တခုရဲ့ AWS region တခုမှာ VPC 5ခုအများဆုံး ထားလို့ရပါတယ်... AZ မဟုတ်ပါဘူး အဲ့ဒါလေးတော့သတိထားရမှာပါ..
peering က one to one ဖြစ်တဲ့အတွက် VPC များလာရင်တော့ configuation complex ဖြစ်လာပါမယ်၊ နောက်တခုကတခြား AWS account တွေရဲ့ VPC နဲ့ချိတ်ဆက်သုံးချင်တာတွေလဲရှိနိုင်ပါတယ် အဲ့လို VPC တွေများလာမယ်ဆိုရင်တော့ Transit Gateway ကိုသုံးတာက ပိုစိတ်ချမ်းသာရပါတယ်။ VPC နည်းသေးတယ် နောင်လဲတိုးလာဖို့ မရှိသေးဘူးဆိုရင်တော့ အခုနည်းလမ်းက ပိုအဆင်ပြေပါတယ်.
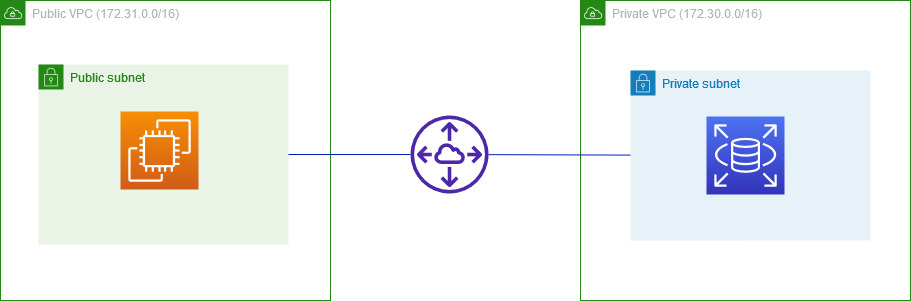
ဆိုတော့ Pubilc VPC နဲ့ Private VPC ဆိုပြီးရှိတယ်ဆိုပါစို့
Pubilc VPC ထဲက webserver က Private VPC ထဲ က database ကိုလှမ်းသုံးချင်တယ်ဆိုရင် အဲ့ဒီ VPC တွေကို peering လုပ်ပေးဖို့လိုပါတယ်..
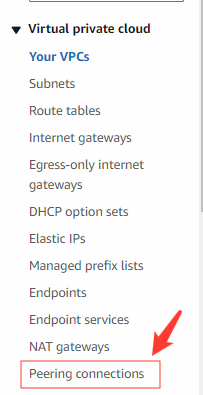
Peering လုပ်မယ်ဆိုရင်တော့ VPC ထဲက peering connections ကိုရွေးရပါမယ်.
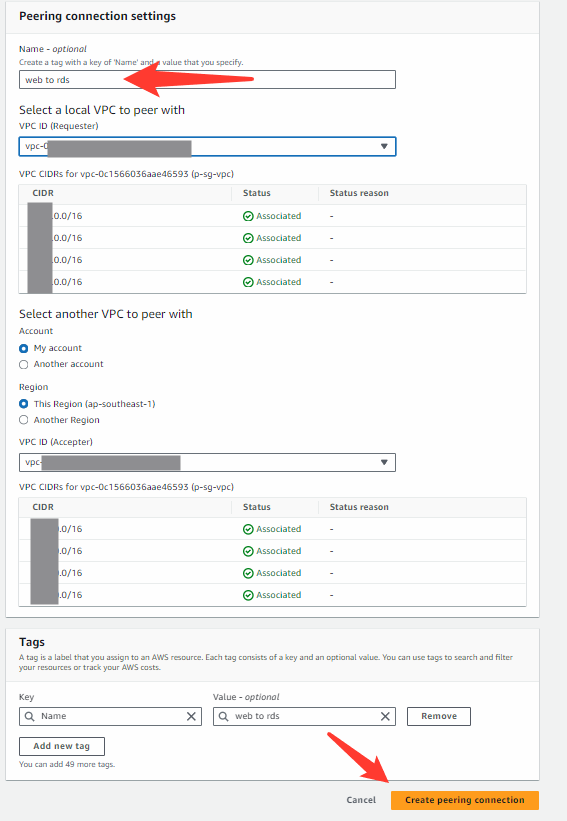
ပြီးရင်တော့ Create peering connections ကို click ပါ၊

ဒီ box ကျလာရင်တော့ name မှာ ပေးချင်တဲ့ နာမည်ရယ် local peering VPC ကိုရွေးပါ၊ ကို့အကောင့်တခုတည်းဆိုရင်တော့ ချိတ်စေချင်တဲ့ VPC ID ကိုရွေးပေးလိုက်လို့ရပါတယ်။ အကယ်၍ တခြား AWS account ဆိုရင်တော့ Account မှာ ကိုချိတ်ချင်တဲ့ account ID နဲ့ region ရယ် VPC ID တို့သိဖို့လိုအပ်ပါတယ်။ အချက်အလက်တွေပြည့်စုံရင်တော့ create peering connections ကို click လုပ်လိုက်ရုံပါပဲ။
AWS account တခုထဲက VPC ချိတ်တာဖြစ်ပေမယ့် peering connection ကို ရွေးပေးပြီး Actions ကနေ Accept request လုပ်ပေးရပါတယ်၊ အကယ်၍ တခြား region တခြား account တွေဆိုလိုရှိရင် accept လုပ်မယ့် VPC ရဲ့ peering connection ထိသွားပြီး accept လုပ်ပေးရပါတယ်

Accept လုပ်ပြီးရင်တော့ status က active ဆိုပြီးပြောင်းသွားမှာဖြစ်ပါတယ်
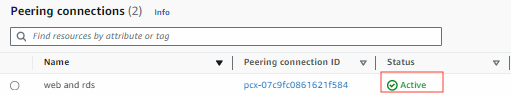
ဒါဆိုရင်တော့ peering လုပ်တာအောင်မြင်သွားပါပြီ။
Connect ဖြစ်ဖို့ကတော့ သက်ဆိုင်ရာ VPC တွေက route table မှာ information ထည့်ပေးရမှာဖြစ်သလို၊ security group နဲ့ NACL မှာ allow လုပ်ပေးဖို့လိုအပ်ပါတယ်..
Thank you...
Zaw
Comments
Post a Comment